#code-review
1 article
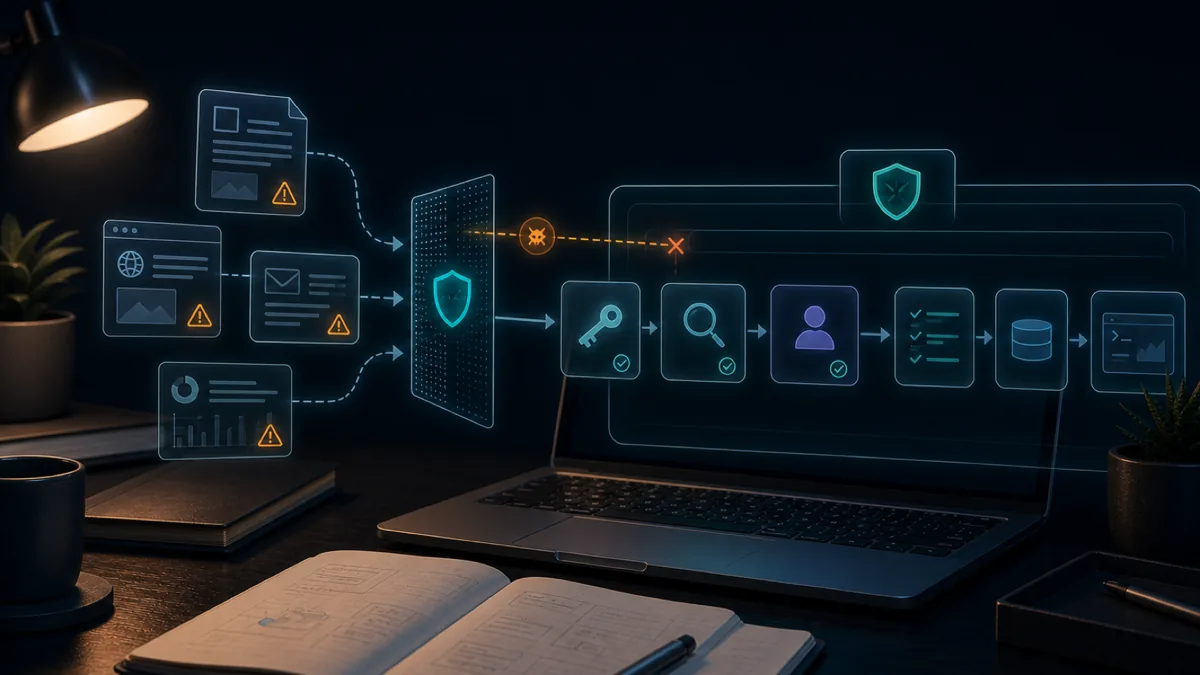
Prompt injection is not an XSS problem
Sanitizing output protects your page. It does nothing for an agent that reads a poisoned README and then runs a command. A practical model of the threat, and what actually helps.
LLM Mart
· Jun 23, 2026
44
views