#devops
9 skills & prompts · 14 tools · 18 MCP servers · 9 articles
Skills & prompts
cron-doctor
Diagnose and validate cron expressions before they ship. Catches the five silent death-traps: impossible dates that never fire, OR-semantics that fire too often, midnight spikes, uneven step drift, and leap-year February 29.
github-runner
Deploy, manage, and troubleshoot self-hosted GitHub Actions runners. Covers systemd service, Docker containers, Kubernetes (Actions Runner Controller), and the Scale Set Client. Use when setting up a CI runner, debugging registration failures, designing autoscaling, or hardening
dockerfile-linter
Checks a Dockerfile for common problems such as unpinned base images, running as root, ADD instead of COPY, secrets in ENV or ARG and apt-get without cleanup. Use when the user asks to review, harden or slim down a Dockerfile.
coolify
Use when self-hosting apps and databases with Coolify on a VPS you own — install, first-admin lockdown, Git-to-deploy (Nixpacks/Dockerfile/compose), managed Postgres/Redis, scheduled S3 backups, domains + auto-SSL. NOT a PaaS someone else runs (that is `railway`), NOT sizing/hard
env-file-auditor
Compares a .env file with its .env.example template and reports missing keys, undocumented extra keys, empty values and example files that contain real looking secrets. Use when the user asks why an app fails on startup with missing configuration, or wants to check environment fi
log-analyzer
Summarizes application log files by severity, time range and the most frequent error messages. Use when the user shares a log file or pasted log output and asks what went wrong, which errors repeat, or how noisy the log is.
docker-compose-reviewer
Reviews a docker-compose.yml for risky or fragile settings such as unpinned images, privileged containers, secrets in environment values, a mounted Docker socket and host networking. Use when the user asks to check, harden or clean up a compose file before deploying a stack.
cron-explainer
Explains a five field cron expression in plain English, validates every field and warns about schedules that can never run, such as February 30. Use when the user pastes a crontab line or a schedule string and asks when it runs, or wants to check a schedule before adding it.
git-automation
Infrastructure skill — Git repository analysis and automation: inspect commits, branches, diffs, and file history. Use when analysing a codebase, reviewing changes, or automating version control workflows independent of any DCC. Not for DCC asset versioning or Perforce operations
Tools
See all 14
Versus Incident is the self-hosted AI SRE agent. It learns what your system normally look like and escalates only what is new or unexpected issues — routing to…
Next-gen AI-native server ops panel with an in-workspace SRE agent. Crash self-healing, safe rollbacks, Docker/game servers, and local Ollama support.
⚡ Control Apache Airflow with natural language via MCP. Chat with your workflows using Claude, GPT, or any LLM — no REST API calls needed. Supports Airflow 2.x…
A CLI-based SSH tool that exposes remote execution, file transfer, connection reuse and command allow/deny lists as local commands callable by agents. 基于 CLI 的…
MCP servers
See all 18Control fleets of remote machines via AI agents: exec, files, git, fleet ops, map/reduce.
Deterministic, offline, read-only ADR decision memory for coding agents. No model or network calls.
Let AI operate servers without SSH. Choose actions, approve risky changes, and audit every step.
Inspect and manage a homelab over MCP - status, Docker, ports, backups - without shell access.
Manage AWS, Hetzner, OVH and SSH servers: status, logs, CloudWatch, IP bans, safe command exec.
A modern, container-friendly, optionally-distributed, fault-tolerant, highly available, leader-electing, highly configurable, precompiled, multi-architecture, p…
Detects database migration table locks, terraform cost leaks, and OWASP API flaws.
Live status-page map for 1,127 SaaS/cloud vendors plus 15,418 historical incidents.
SDK for creating, managing, and operating Kubernetes clusters and workloads with ease.
Enfour, Inc. FrontierStack (www.frontierstack.app): Mac and server health, logs, restarts.
Articles
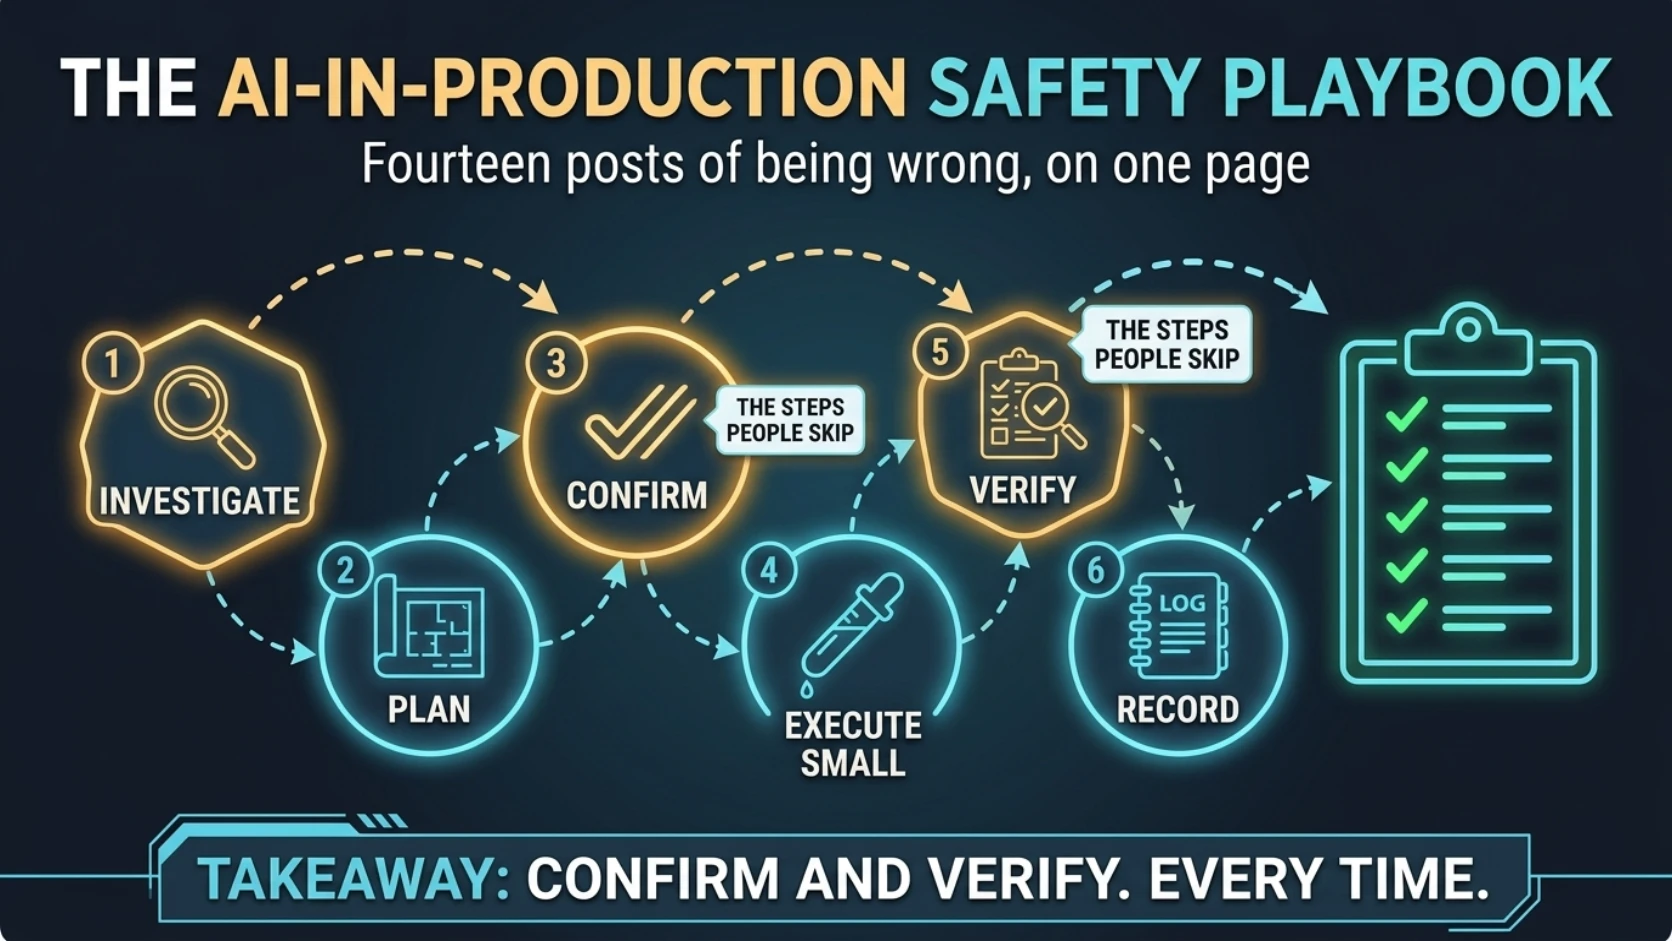
The AI-in-production safety playbook
Fourteen posts of being wrong in production, compressed to checkboxes
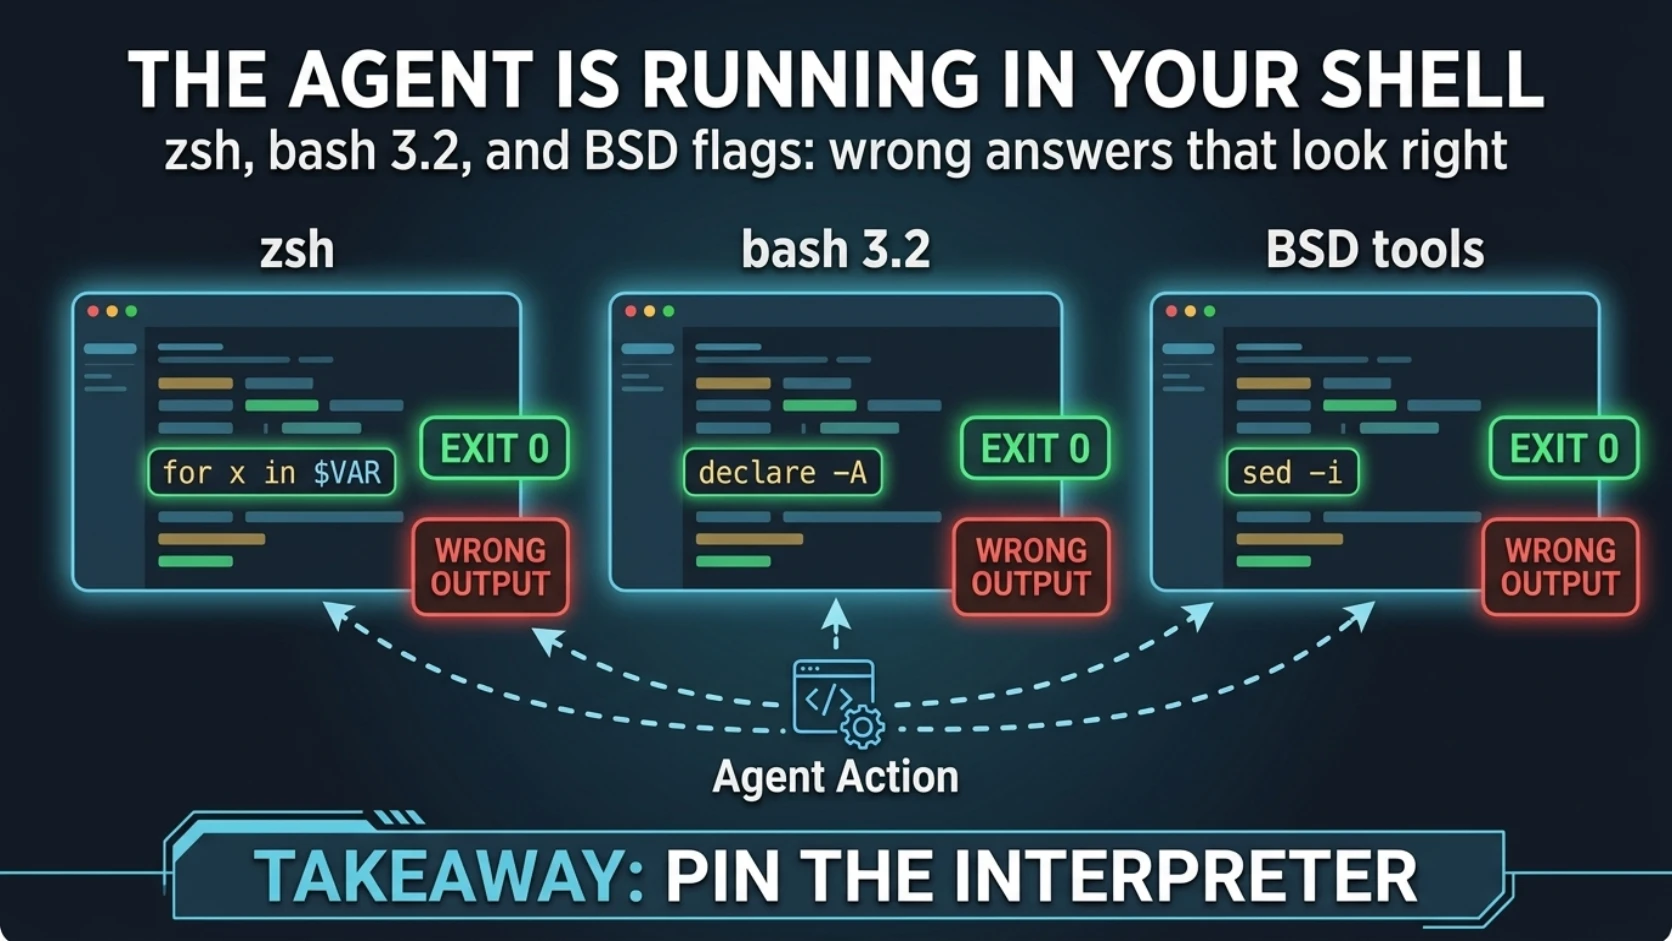
The agent is running in *your* shell
A surprising share of AI-in-the-terminal failures aren't the AI. They're zsh, and a version of bash from 2006.
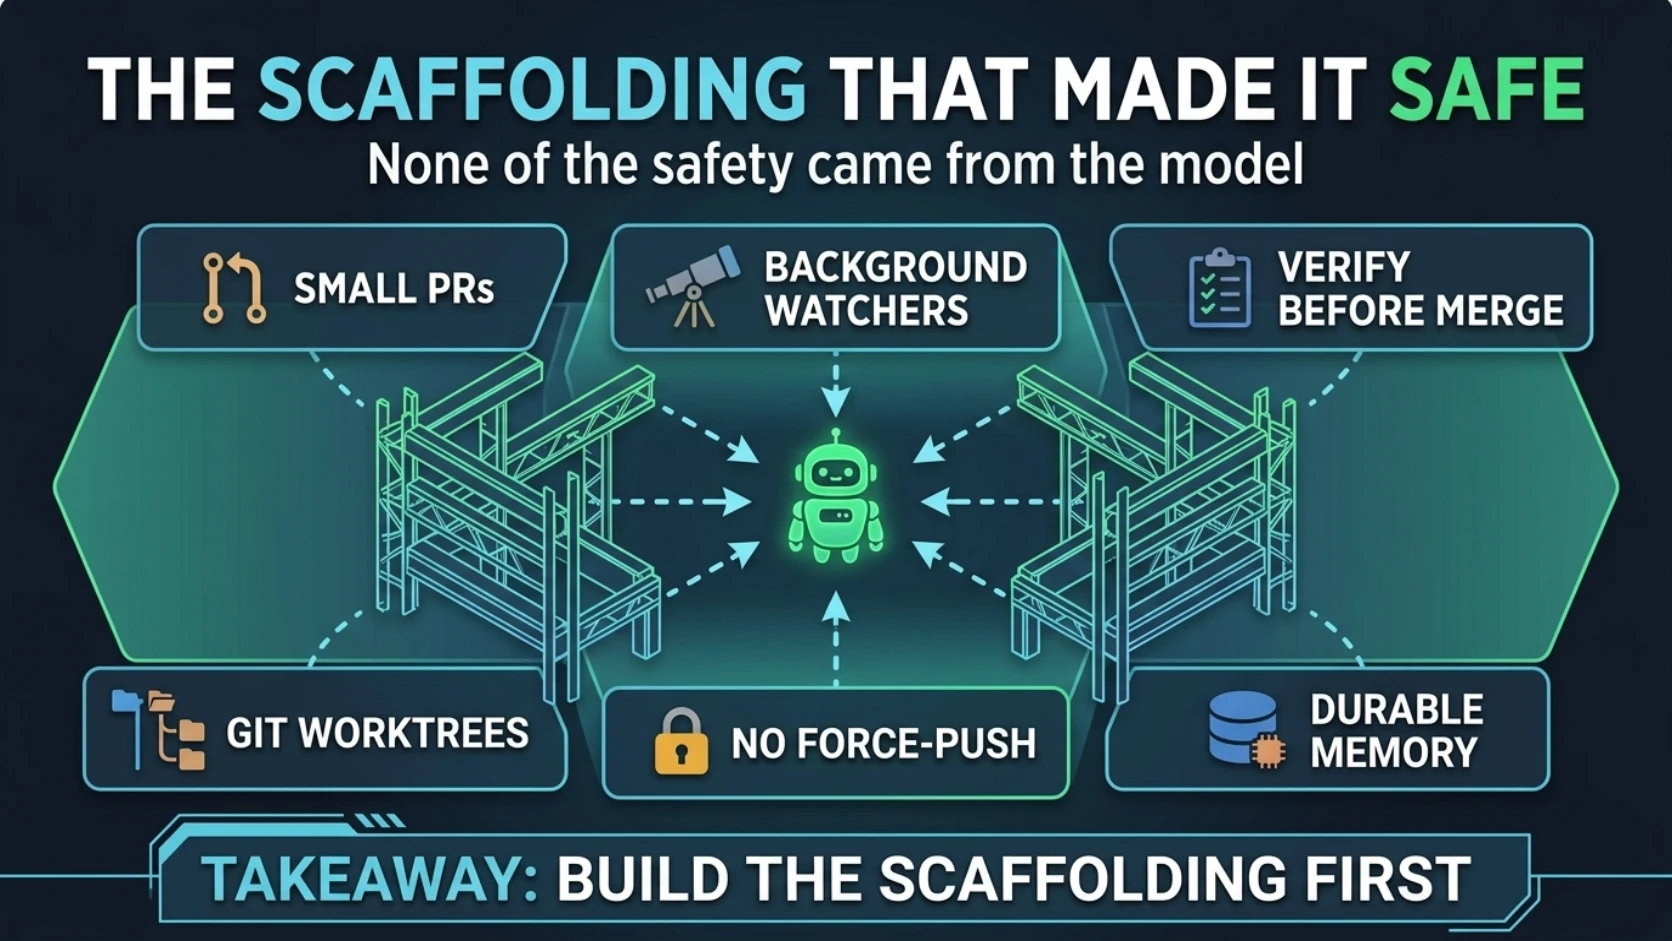
The scaffolding that made it safe
None of the safety came from the model. It came from six boring habits.
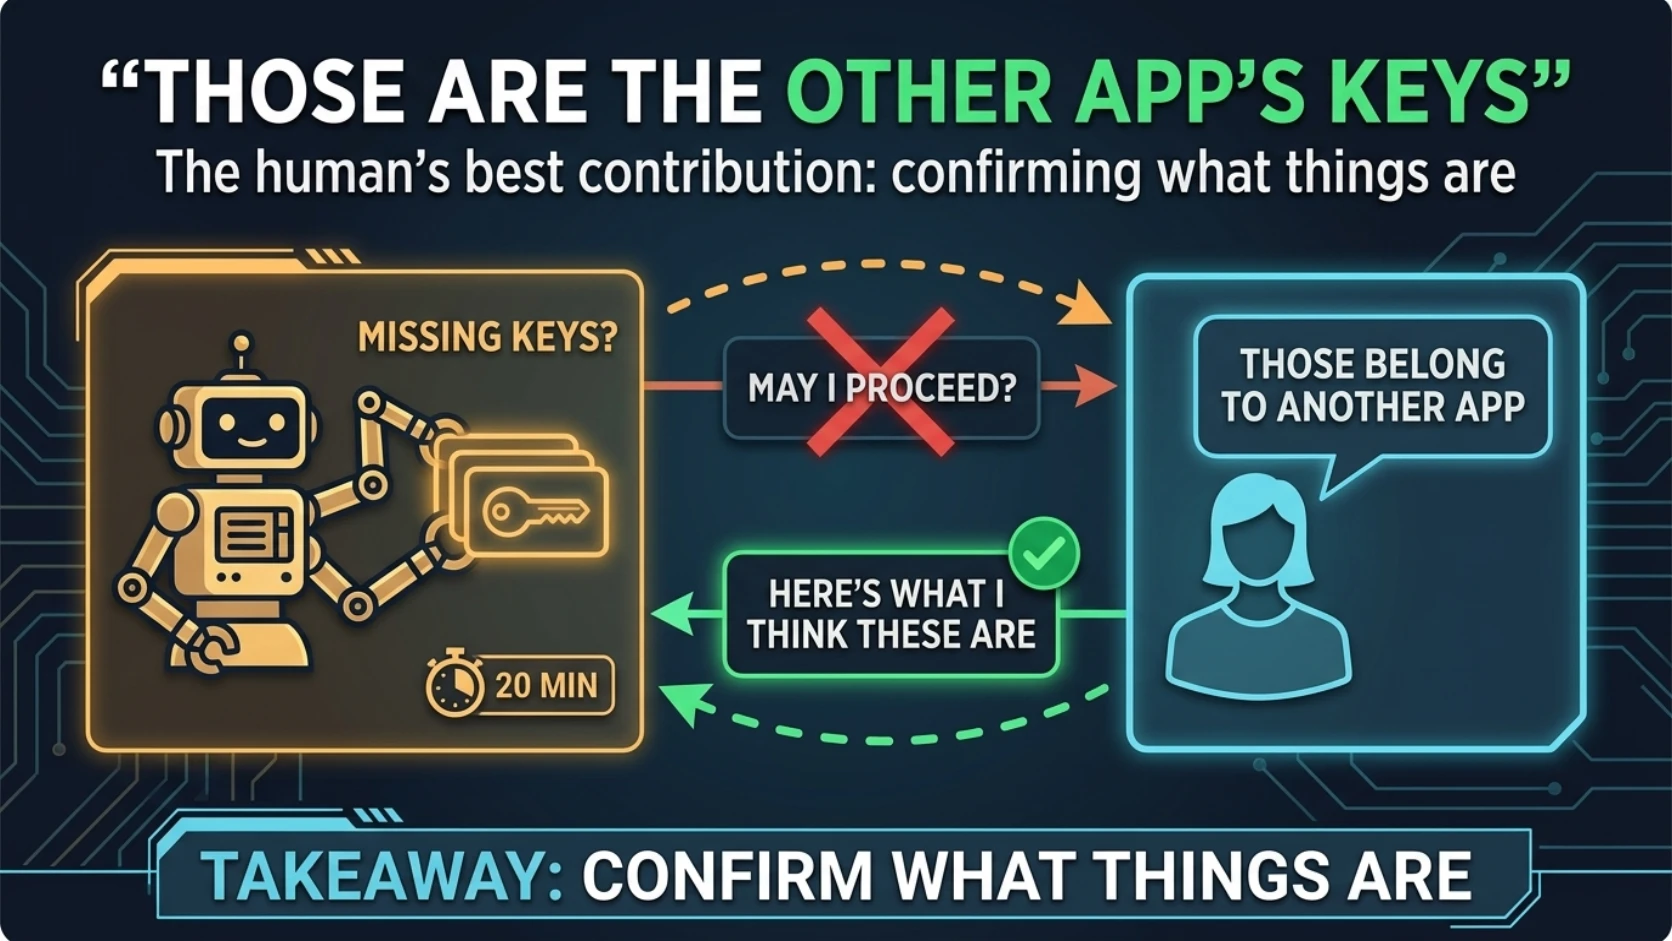
Those are the other app's keys
Twenty minutes recovering secrets that never existed, and the one sentence from a human that ended it
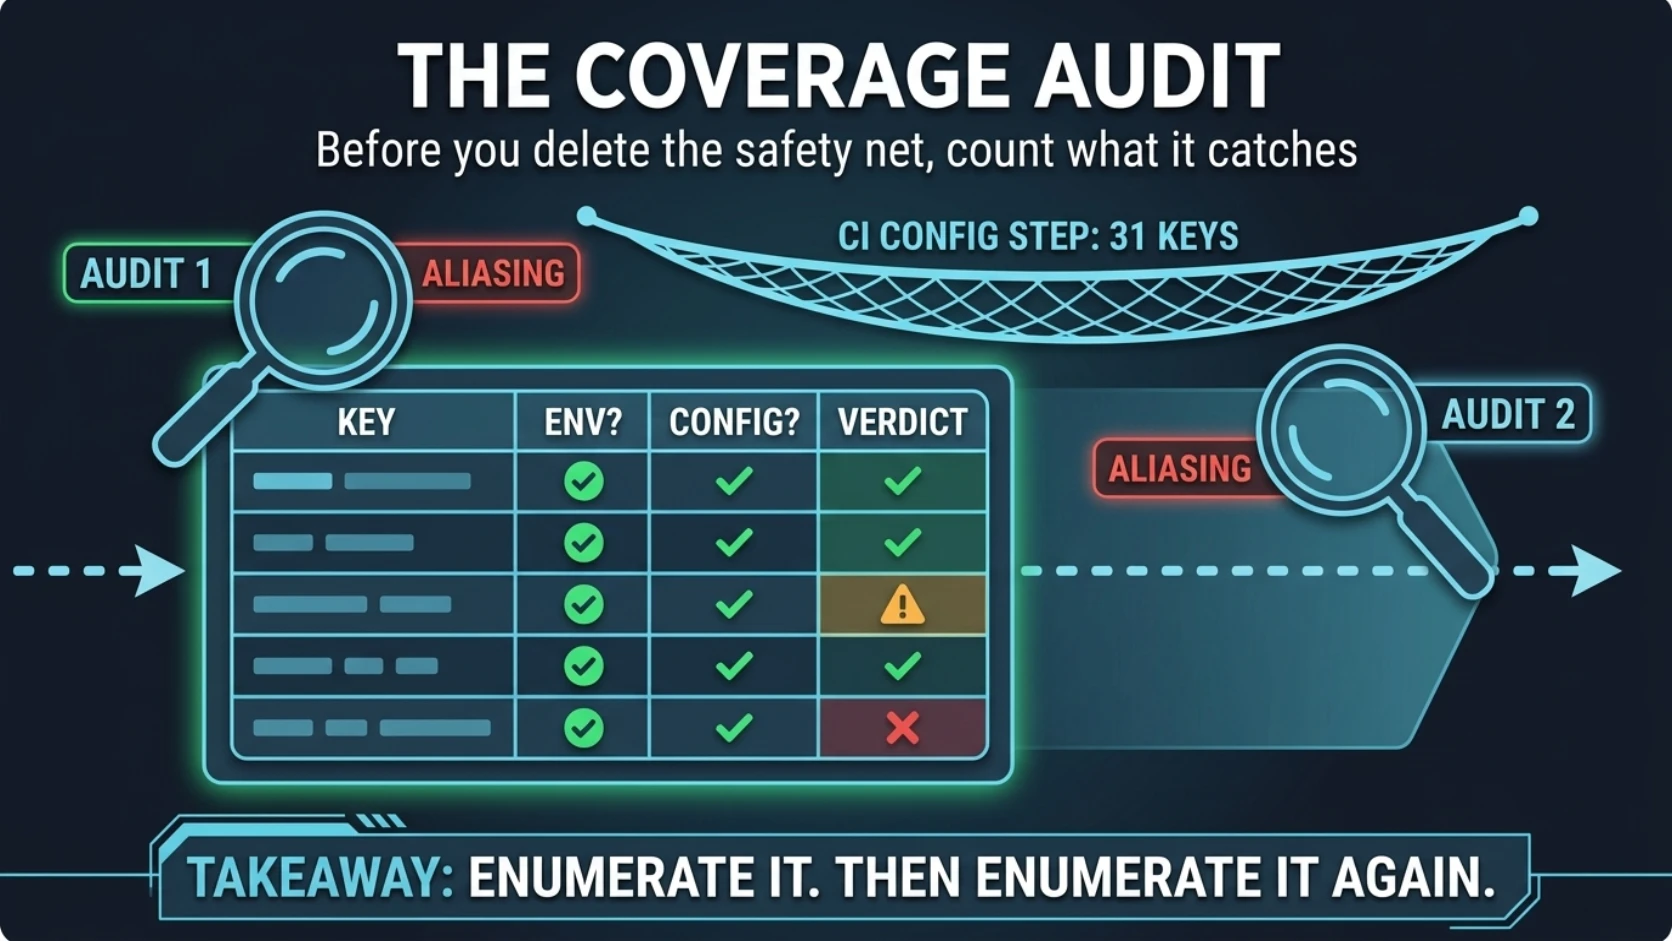
The coverage audit before you delete the safety net
31 config keys, two audits, and why the first one was wrong in both directions
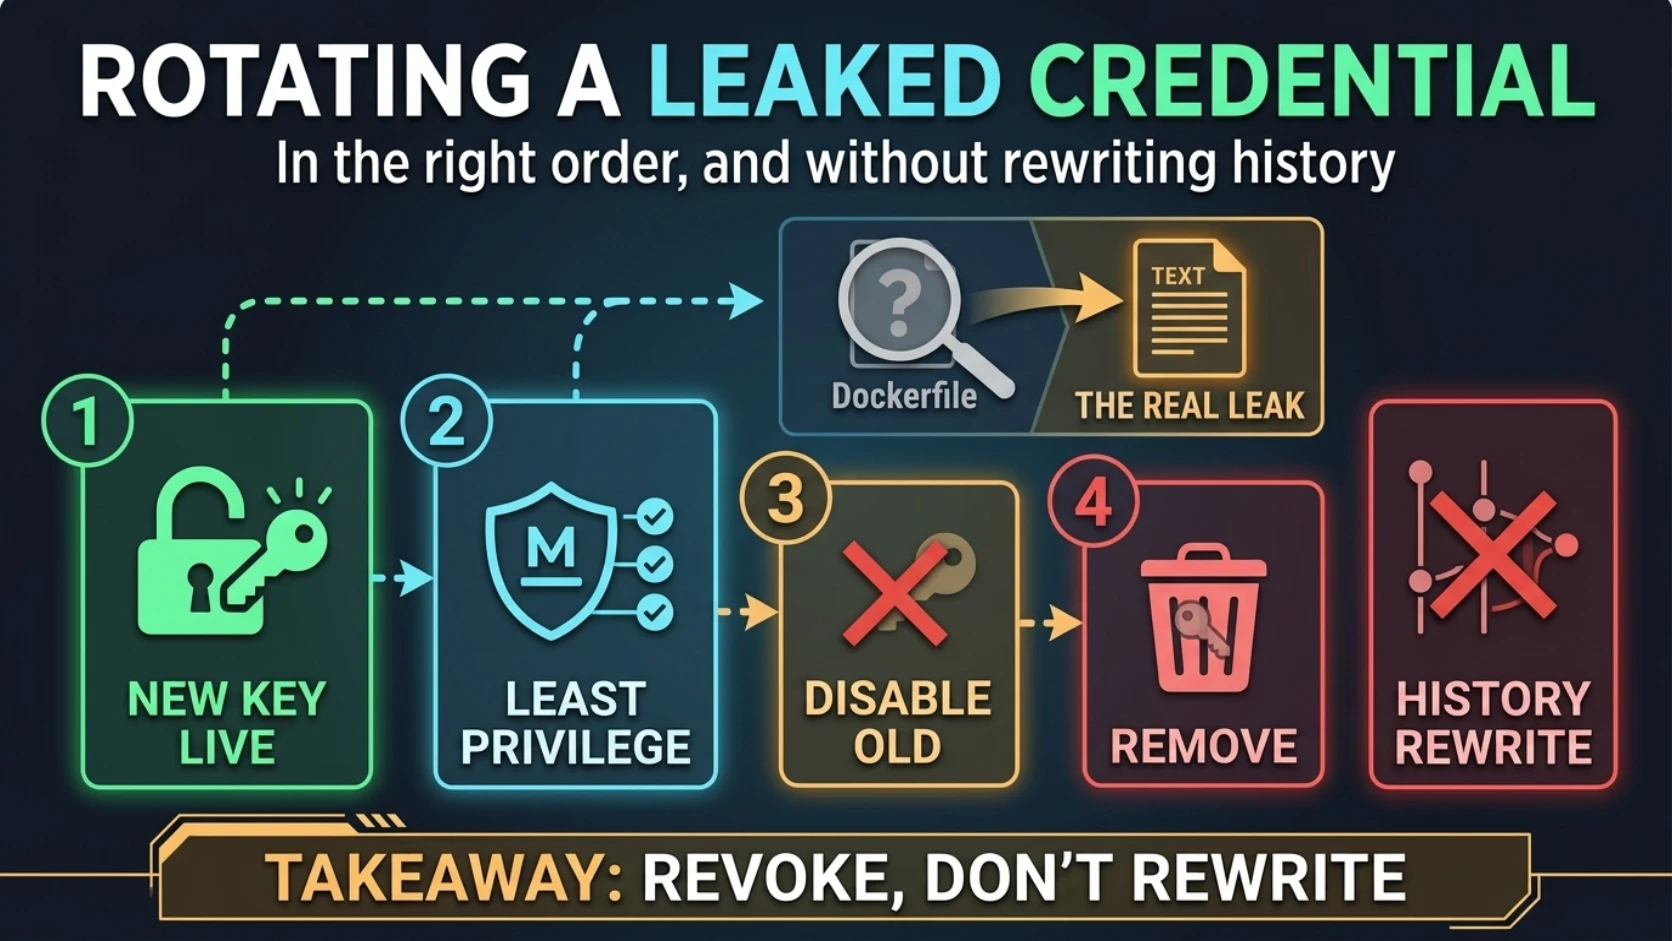
Rotating a leaked credential, in the right order
Everyone looks at the Dockerfile. The file that actually leaked the key was the project file.
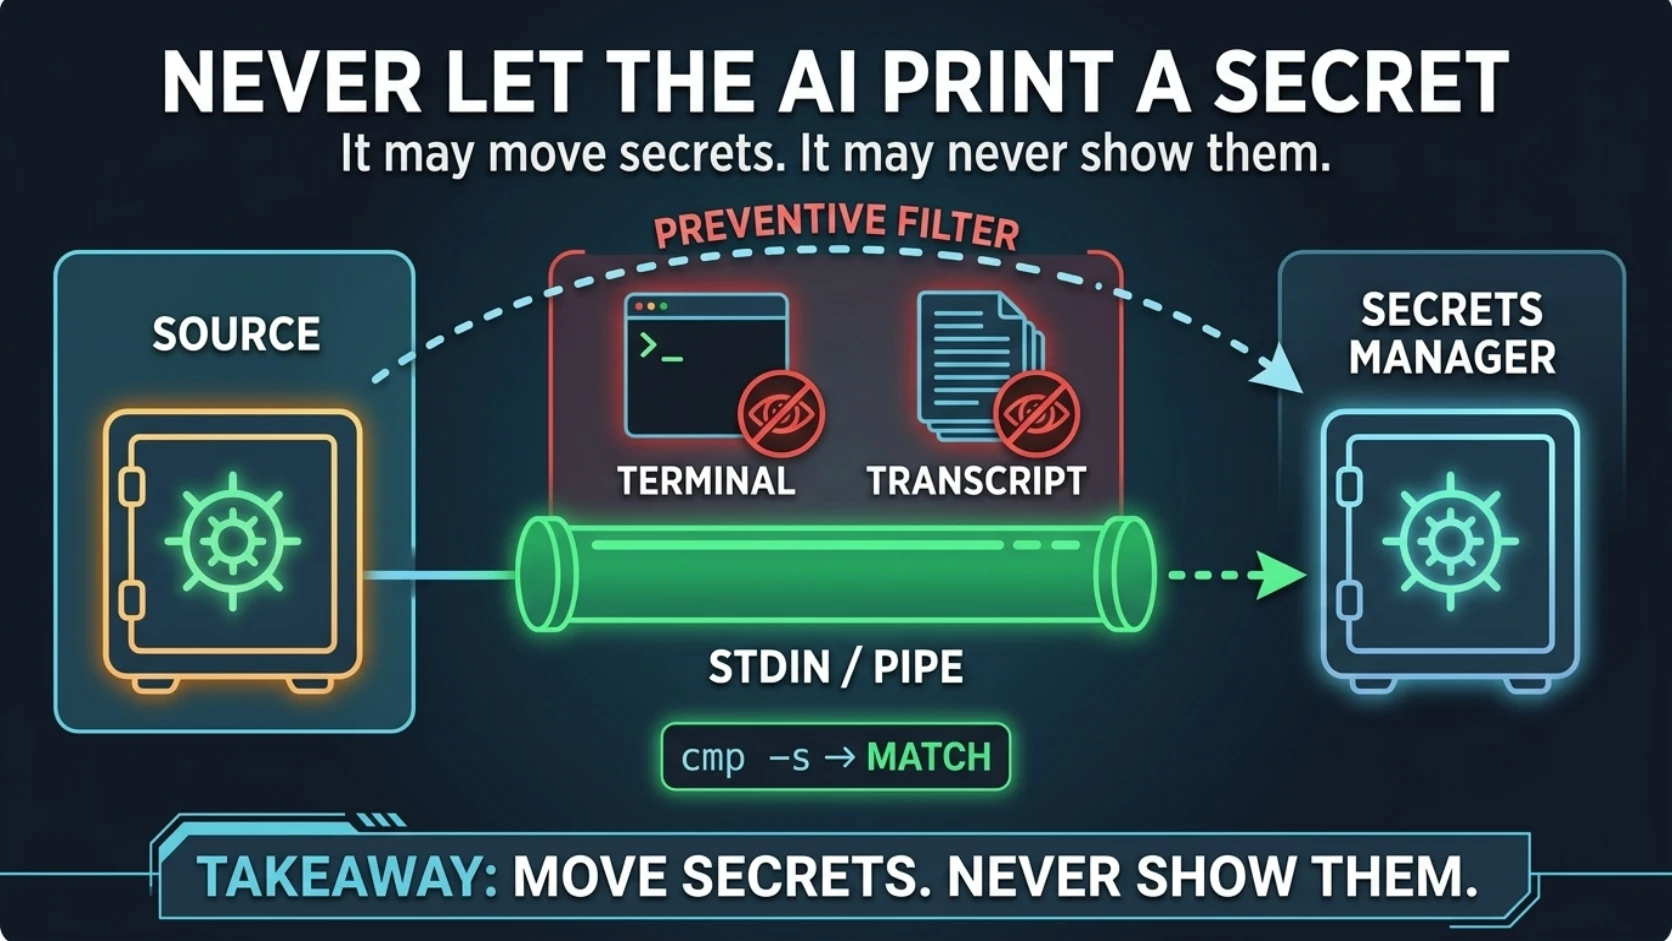
Never let the AI print a secret
The most important rule wasn't about what I could change. It was about what I was allowed to display.
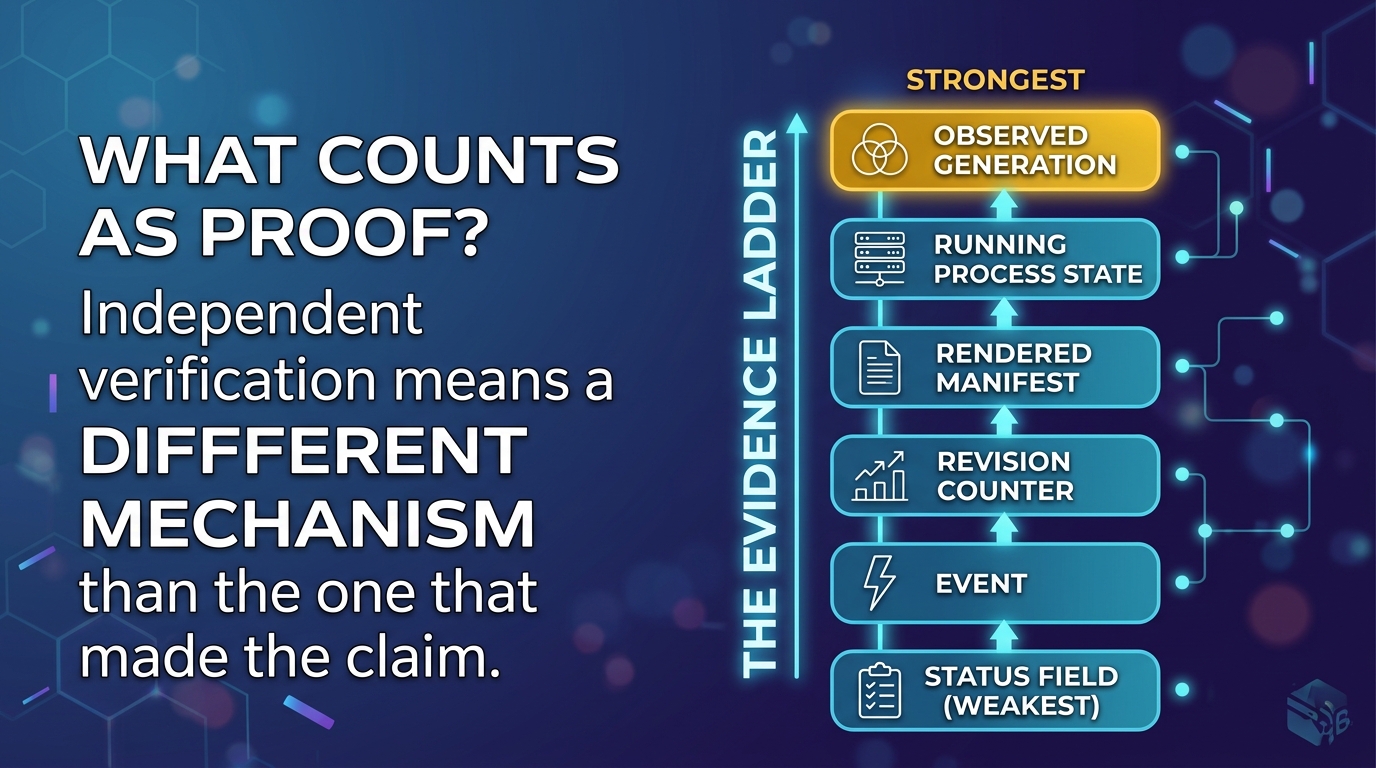
What counts as proof
"Verify your work" isn't an instruction. It's a mood. Here's the version that's an instruction. Verify with a different mechanism than the one that made the claim.
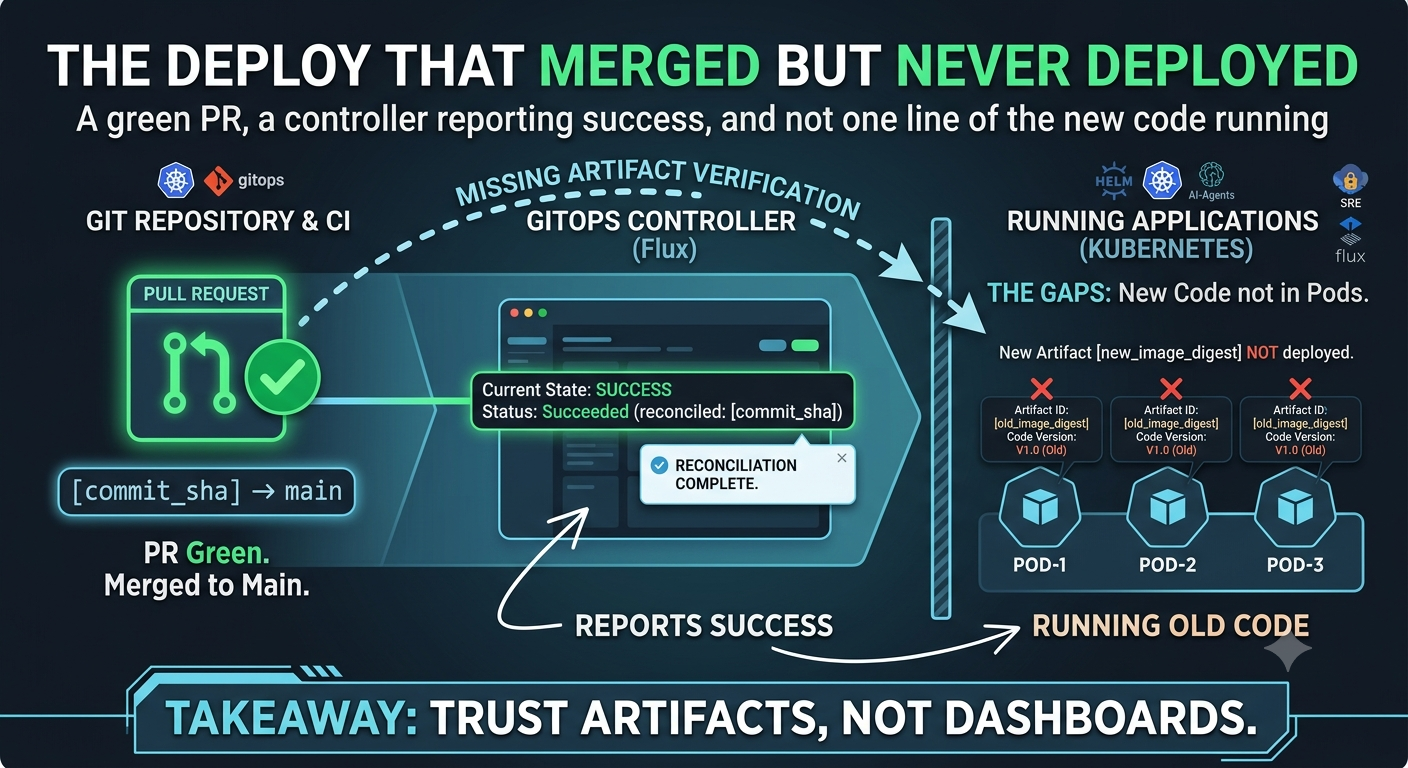
The deploy that merged but never deployed
A green PR, a controller reporting success, and not one line of the new code running